
Cybersecurity for
SaaS, Companies and Organizations
There are bots scanning the internet for breaches 24/7. We help companies and organizations close real breaches before one of them finds yours.
See all services →Get your free diagnostic
Every minute without a diagnostic is an open window. We respond within 1h.
✓ Request received
We'll review your request and get back to you within 1h.
🔒 Your data is never shared with third parties.
Your company might be exposed right now, and you don't know it.
Automated tools scan the entire internet 24 hours a day, non-stop.
It's not a hoodie-wearing hacker watching you. It's worse: it's thousands of automated bots running non-stop, knocking on every door on the internet, all day, without picking anyone in particular. Just waiting to find yours unlocked. And sometimes that takes minutes.
Most companies only discover the flaw after it's already been exploited. We're offensive security specialists. We find the real breach in your system before an attacker does, and we close it for good.
I want to know where I'm exposedIt's not one attack.
It's thousands, all the time.
While you scroll this page, this is already happening to your system too.
It never stops. Ever.
I want to know if they already found meVultx Security doesn't hand you a PDF and disappear
We're offensive security specialists for SaaS and B2B startups. We find the real flaw in the application, API, or cloud infrastructure, and we close the door in the architecture.
We work with SaaS companies that already know they have exposure in production, but don't have anyone to close the full loop: from the technical finding to the architectural and governance decision, with no handoff between whoever finds it and whoever fixes it, and without the weight of a generic pentest built for a bank's corporate network.
Researcher-Grade Diagnosis
Methodology from someone who hunts vulnerabilities in real bug bounty programs, not an automated checklist.
No Handoff
Whoever finds the flaw is who designs the architectural fix. No context gets lost along the way.
Continuous Governance
Risk prioritization, board reporting, and remediation follow-through until the end.
Do you know where your company is exposed right now?
Find out in days, not months, with a diagnostic based on CIS Controls v8, the most widely used security framework in the world.
Express Diagnostic
A quick check of the 5-6 most critical security points in your company. 30-minute conversation, report within 2 business days.
- 30-min conversation with a specialist
- Straight-to-the-point report, no jargon
- Clear recommendation for the next step
CIS v8 Maturity Assessment
Full evaluation of the 18 CIS v8 security controls, with a prioritized action plan and a live results presentation.
- Evaluation of the 18 international controls
- Risk report in business language
- Action plan prioritized by urgency
- Live presentation with the specialist
Complete offensive security for your SaaS
Pick the service that solves your need right now. Each one becomes a custom quote request, no fine print.
Web Application Penetration Testing
Manual offensive testing on your application, looking for the same flaws a real attacker would exploit.
API Penetration Testing
REST/GraphQL API security: authentication, authorization, data exposure, and business logic.
Cloud & Infrastructure Penetration Testing
Cloud configuration assessment (AWS/GCP/Azure), network, and external attack surface.
Source Code Review
Manual source code review looking for vulnerabilities no scanner finds on its own.
Red Team Exercise
Real, end-to-end attack simulation, testing people, process, and technology together.
Purple Team / TTPs
Collaborative attack-defense exercise, simulating real adversary tactics (MITRE ATT&CK).
Social Engineering Testing
Controlled phishing and pretexting, to measure how well your team resists manipulation.
Bug Bounty Program Management
Vulnerability reward program management, from triage to remediation.
Fractional CISO/CTO
Security and architecture leadership on demand: risk prioritization and remediation, without a full-time hire.
Flaws we found and fixed
Real findings, anonymized, no client or program name.
SSRF in an enterprise platform
Server-Side Request Forgery with access to internal cloud metadata (public bug bounty program).
FixedAuthentication bypass in a fintech
SAML signature validation flaw allowing identity impersonation on a payments platform.
FixedIDOR in a B2B marketplace
Direct object reference with no ownership check, exposing other clients' order data.
FixedMultisite network compromise via an outdated plugin
A vulnerability in an outdated CMS plugin allowed mass creation of 69 fake admin accounts and hijacking of the master account across a network of 12 sites sharing the same infrastructure. Incident response following NIST SP 800-61, with a surgical fix instead of a full migration.
FixedOffensive security built for the SaaS stack
Methodology from an active bug bounty researcher applied to your web application, API, and cloud infrastructure, not an automated scanner checklist, and not a generic pentest built for a bank's corporate network.
We map your entire SaaS
Web application, API, and cloud infrastructure: we test how a real attacker sees your system, not just what a scanner finds.
We find the real flaw
Manual exploitation, with the same technique bug bounty hunters use. No generic automated tool report.
We fix it with you
We don't stop at the PDF. We help close the breach in the architecture, with a prioritized action plan until the problem is gone for good.
Documented confidentiality process, from NDA to report delivery.
Before touching any of your systems, there's a signed NDA and testing scope (Rules of Engagement). From collection to delivery, every piece of evidence follows a documented chain of custody.
- Isolated testing environment per client, never shared
- Full-disk encryption, evidence stored in an encrypted vault
- Raw evidence wiped after the final report is delivered
- NDA and Rules of Engagement signed before any test begins
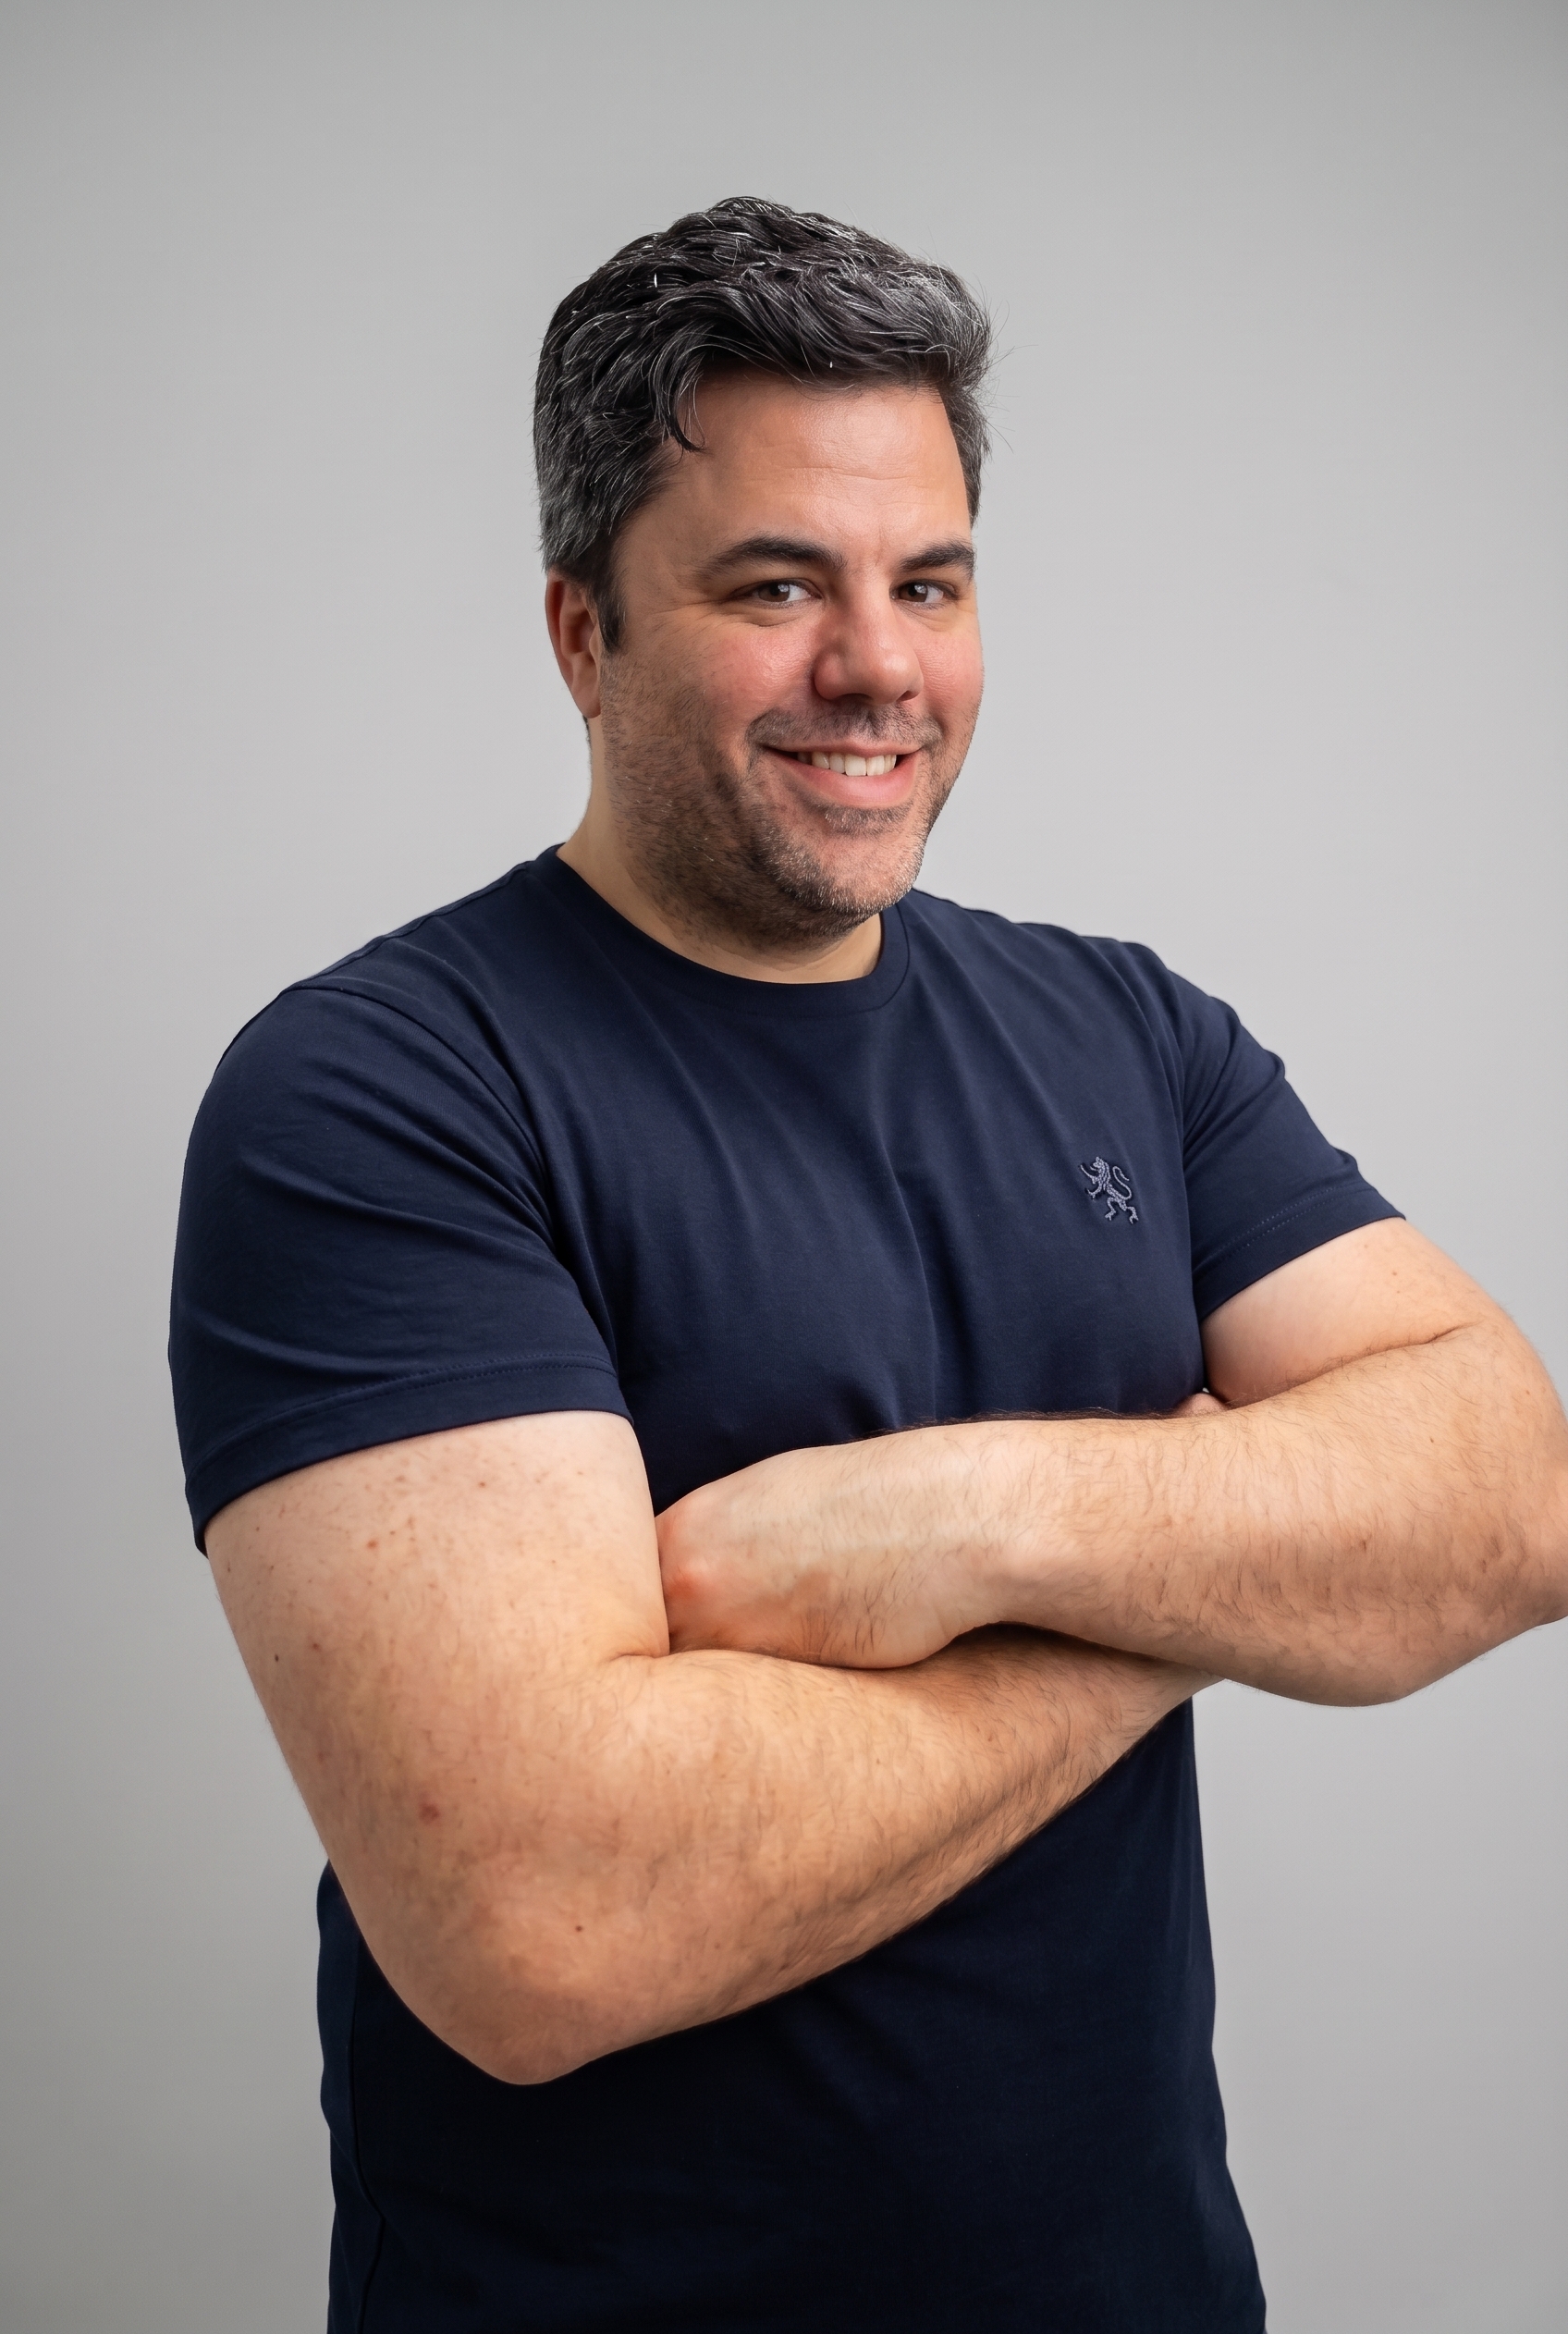
Gabriel Sanabria
Founder, CISO & Fractional CTO
Active researcher in multiple public bug bounty programs, with dozens of critical vulnerabilities reported in production: from SSRF and authentication flaws to privilege escalation in APIs.
IT executive with 20 years of experience and a member of ISACA. Previously led technology, security, websites, and systems for Brazil's largest pizza chain. Today he works as Infra Ops & Security Lead for a multi-tenant SaaS platform used by major retail and pharmacy chains in Brazil, among other clients, in addition to managing website infrastructure for more than 100 shopping malls across the country.
Before Vultx Security, he co-founded and led the technology of a B2B fashiontech company with significant institutional funding and a strategic exit in 2020.
He mentors founders at the Brazilian Startup Association (ABStartups) on digital business, infrastructure, and SaaS security, teaches the university extension course at EFPD (Digital Products Training School), certified by Faculdade CTA, and is an ORCID-registered researcher, author of a paper on Outcome-as-a-Service (OaaS) published on SSRN. It's this mix of research, operating at scale, and business vision that grounds Vultx Security: security thought through from inside the system, not a generic outside report.
In the media
The founder's technical journey, covering technology, entrepreneurship, and leadership.
FashionTech Startup Raises US$2.1 Million, Eyes B2B Expansion
The institutional funding climb and capital-raising journey led by Gabriel up to the exit.
PEGNHow Technology Is Transforming Brazil's Fashion Market
Analysis on pioneering B2B transactional platforms and scalable retail infrastructure.
ISTOÉ DINHEIROThe New Models of Technical Leadership Investors Are Demanding
Strategic discussion on the evolution of technical governance models in high-growth startups.
EstadãoArtificial Intelligence and Governance: the Challenge of Operating at Scale
Debate focused on AI security, operational risk mitigation, and autonomous agent orchestration.
terraTech Entrepreneurship: from Software Architecture to Business Outcomes
The strategic transition from pure technical building to effectively delivering commercial outcomes.
From the blog
Real anonymized cases and practical offensive security guides for SaaS, straight from someone who hunts vulnerabilities in production.
Run a security audit on your SaaS with AI, using a ready-made prompt
A structured prompt to paste into ChatGPT, Claude, or Gemini to uncover the most common risks in your SaaS before you get hit.
SSRF: how a simple flaw exposed cloud metadata on an enterprise platform
What SSRF is, why it's so dangerous in a cloud environment, and how to fix it.
IDOR: why "only the owner can see it" has to be enforced on the backend
How this flaw exposed other clients' orders in a B2B marketplace, and why it's the most common mistake in SaaS.
Let's find the flaw before the attacker does.
Web, API, or cloud infrastructure pentest, red team, or fractional CISO/CTO: describe your SaaS and stack, and we'll get back to you with next steps.
✓ Request received
We'll review your request and get back to you with the next steps of the diagnostic.